

CoreWeave launched Physical AI Launchables and the CoreWeave Zero Trust AI Framework today at NVIDIA GTC Berlin. Launchables is a catalog of tested, ready-to-run templates for robotics and autonomous vehicle tools, each started with one command, that pairs environments for NVIDIA Isaac Sim, CARLA, MuJoCo, NVIDIA AlpaSim, and NVIDIA Cosmos 3 with coding-agent skills tuned to CoreWeave’s cloud. The Zero Trust framework is the security half of the announcement: six controls that keep encryption keys, administrative access, and model data under the customer’s authority.
Five Tool Templates and Cosmos Data Factory Skills
At launch, the catalog covers five tools. Isaac Sim ships four templates: a Franka pick-and-place task, a forklift-and-pallet scene with labeled synthetic data, vehicle-dynamics variants with driving and braking trajectories, and a warehouse with workers and incidents captured by multiple cameras. CARLA gets a driving-scenario matrix, MuJoCo a GPU-parallel reinforcement learning sweep on MuJoCo Warp and a RoboCasa kitchen task, AlpaSim a closed-loop evaluation of NVIDIA’s Alpamayo driving model over reconstructed real scenes, and Cosmos 3 a text-to-video scenario generator on Cosmos 3 Nano. Every tool also ships a blank template for workloads the catalog does not cover, and a Voxel51 FiftyOne template is listed as coming soon.
Settings change as name=value pairs on the command line (scenarios, duration, parallelism, the model under test), and bigger changes go into the template’s application code; CoreWeave’s Isaac Sim example launches each hand-edited variation in about 30 seconds. The catalog also integrates NVIDIA Cosmos Data Factory agentic skills for auto-labeling, data curation, retrieval, and generative augmentation across video, image, and text, with more Cosmos Data Factory workflows promised as templates.
Decoupled CPU Stages, Agent Skills, and ISV Partners
Where a workload allows it, the templates run CPU-only preparation and post-processing before GPU execution begins and release the GPU nodes as soon as the accelerated stage ends. Each template declares its resource and concurrency limits so parallel runs do not compete for the same host, states its inputs and what it returns, and sends reports, metrics, media, and diagnostics back through one interface. Every operation is documented, and every response is machine-readable, so a script or a coding agent can launch, monitor, and retrieve a run.
CoreWeave ships agent skills tuned to its cloud with every template, alongside the reference physical AI skills NVIDIA publishes for any cloud, and they work with Claude Code, Codex, and other coding agents. Humans and agents share the same visible workflow of inputs, settings, runs, and results, so an agent’s changes can be inspected and traced. On the partner side, Cadence, Convergent Science, Encord, nTop, PhysicsX, and Voxel51 run their applications on CoreWeave compute while keeping their interfaces, and customers can run a sustained program on reserved capacity or a single burst job to test one idea.
Six-Layer Zero Trust Framework Isolates Keys, Compute, and Network Paths
The CoreWeave Zero Trust AI Framework sets six control boundaries around enterprise data, model weights, and multi-tenant runtimes, on the premise that agentic AI spreads sensitive data across prompts, embeddings, weights, traces, outputs, and runtime systems. “Security for AI workloads cannot rest on a provider’s promises about its own behavior,” said Chen Goldberg, executive vice president of product and engineering at CoreWeave.
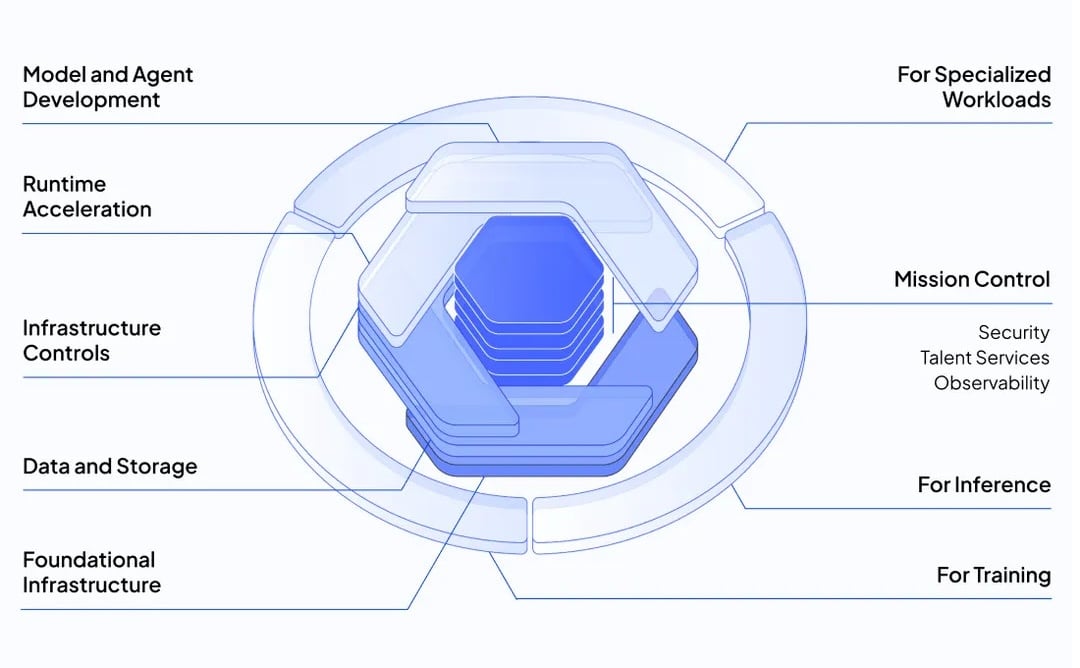
Zero Key Access (Remote Key Encryption) keeps keys in the customer’s infrastructure, whether a software key manager, a hardware security module, or a KMS in another cloud, with no key authority transferred to CoreWeave. Zero Node Access (Support Access Management) makes provider access an explicit customer decision, scoped to a defined operational need and ended when that work is complete. Zero Trust Infrastructure uses hardware roots of trust and CoreWeave’s attestation services, so a key manager, orchestrator, or workload can demand valid attestation evidence before releasing secrets, decrypting data, or proceeding.
Zero In-Use Access is confidential computing. CoreWeave intends to support it on NVIDIA Blackwell and Vera Rubin, with 베라 루빈 NVL72 extending NVIDIA’s third-generation confidential computing across CPUs, GPUs, and the NVLink fabric, and HGX Rubin NVL8 due on CoreWeave Cloud in Q4 2026, starting with select bare-metal environments before Kubernetes-based workloads. CoreWeave also plans to support the NVIDIA 오픈쉘 reference architecture, which pairs Rubin GPUs and Vera CPUs running the OpenShell secure runtime.
Zero Model Data states that CoreWeave, as an AI cloud and not a model provider, does not use customer prompts, training data, model weights, or outputs to train or improve models of its own. Zero Trust Network Encryption runs IEEE 802.1AE MACsec across CoreWeave’s backbone, so encrypted transport comes with the network and no application team has to build it. CoreWeave gives no availability dates for the framework’s layers beyond the Q4 2026 HGX Rubin NVL8 arrival.


 아마존